Industries
Cybersecurity and GRC for regulated, high-impact environments
Quantissimo Investments supports organizations where availability, confidentiality, and compliance are non-negotiable—delivering VAPT, cloud security, SOC as a Service, audits, and governance programs aligned to your operating and regulatory realities.
Industries we serve
We tailor security architecture, testing, and assurance to the threat landscape, technology stack, and compliance obligations of each sector.
Financial Services
Protect customer data, payment systems, and core banking platforms with risk-based testing, monitoring, and control assurance.
Government & Public Sector
Strengthen national and agency security posture with resilient architectures, incident readiness, and compliance-aligned programs.
Healthcare
Secure clinical systems and sensitive records while supporting uptime, privacy obligations, and third-party risk management.
Telecommunications
Reduce exposure across networks and critical infrastructure with continuous monitoring, segmentation, and targeted assessments.
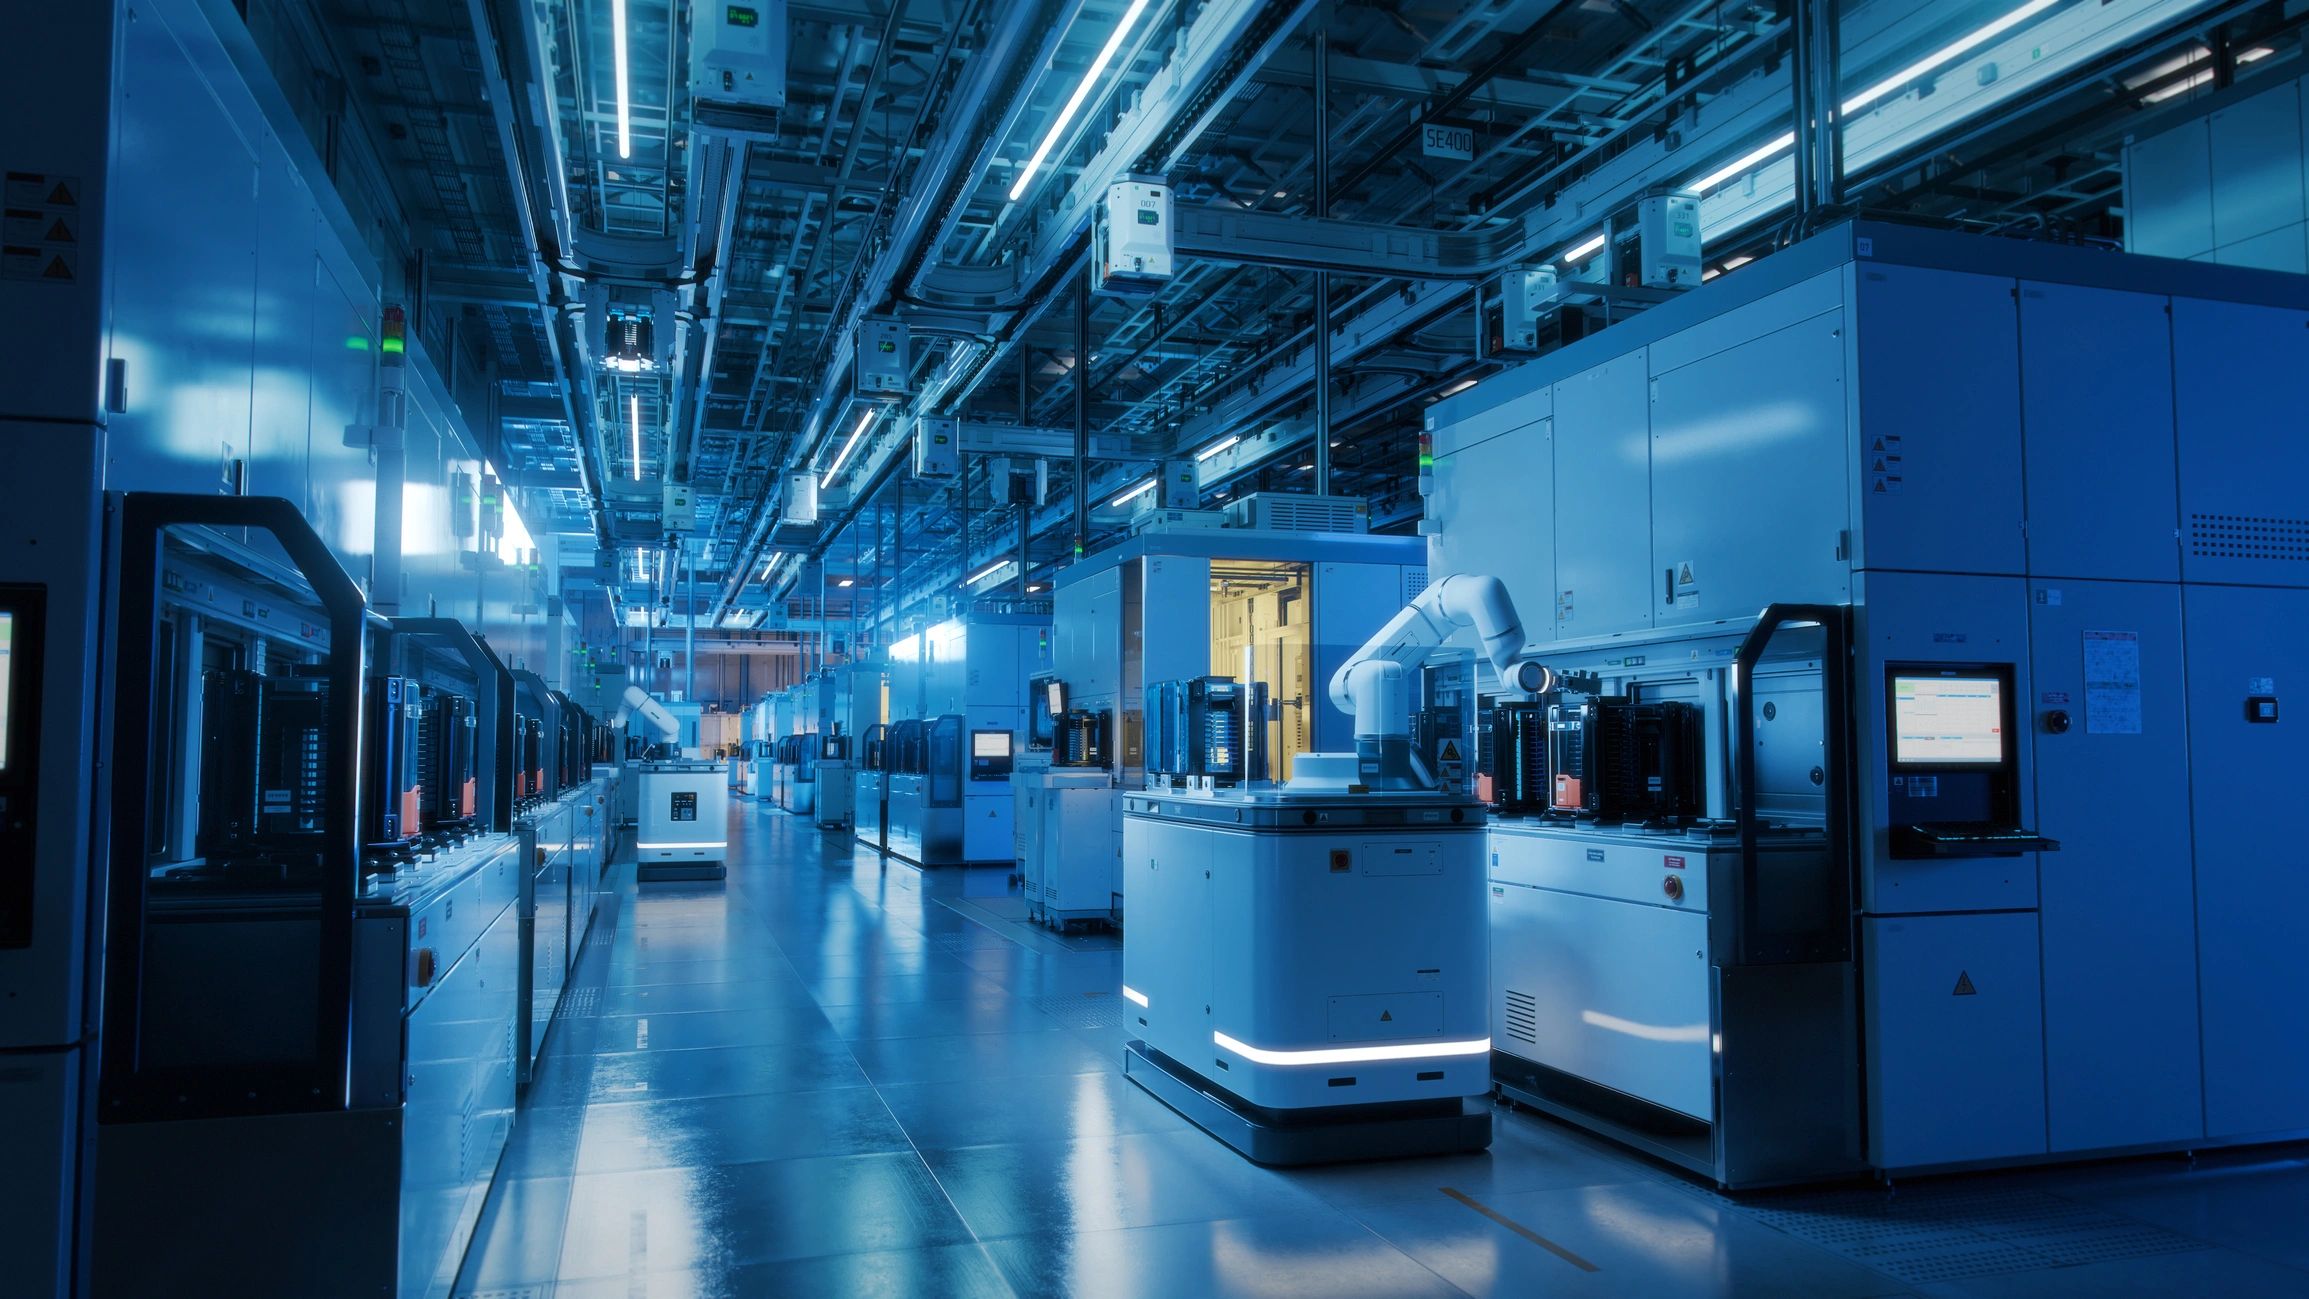
Manufacturing & Industrial
Improve OT/IT security with assessments, hardening guidance, and incident response planning for industrial environments.
Enterprise & Digital Transformation
Enable secure cloud adoption and modernization with zero trust principles, governance, and measurable security roadmaps.
How we engage
A delivery model built for assurance and outcomes
From discovery to remediation support, we align technical work with governance, risk, and compliance requirements—so stakeholders can make decisions with confidence.
✔
Risk-based scope and clear reporting
We prioritize what matters most to your business, mapping findings to impact, likelihood, and practical remediation steps.
✔
Compliance-ready evidence and traceability
Outputs designed to support audits and oversight, with documentation that aligns to common frameworks and regulatory expectations.
Ready to reduce risk?
Get a sector-specific security assessment
Tell us your environment and regulatory context. We will recommend a right-sized approach—VAPT, cloud security, SOC as a Service, audits, or GRC—built for measurable risk reduction.